
What’s included
- Network and firewall review: rules, open ports, remote access and firmware
- Vulnerability scans of servers, network devices and systems facing the internet
- Microsoft 365 review: multi-factor sign-in, admin roles, sharing and email records
- Wi-Fi security: encryption, guest separation and default passwords
- Backup review, including a test restore
- Physical checks of server rooms and network racks
- A written report ranked by risk, with clear fixes
- Help to make the fixes, or a check after your team makes them
How we deliver
- Scope We agree what to cover and set rules for testing.
- Collect We gather settings and run scans at agreed times.
- Review We check findings against a structured checklist.
- Report You get a short report: what we found, why it matters, how to fix it.
- Fix We help fix the urgent items first.
- Recheck We check the fixes and close the findings.
A report you can act on
Long scan reports full of red items get filed and forgotten. We rank findings by real risk to your organisation, explain each one in plain words, and say exactly what to change.
What we check against
Our checklist draws on recognised good practice such as the CIS Critical Security Controls, scaled to the size of your organisation. If you are working towards ISO 27001 or answering a client’s security questionnaire, we map our findings to those requirements.
When you need a formal audit
Some regulators and clients require an audit by a CERT-In empanelled auditor or a certification body. Our assessment is not that audit. It is a good way to find and fix problems before one.
What affects the price
Every quote is built from your site. These are the things that change the number.
- The number of sites and systems in scope
- Whether Microsoft 365 is included
- Scans of systems facing the internet
- How much help you want with fixes
Sectors we serve
Related projects
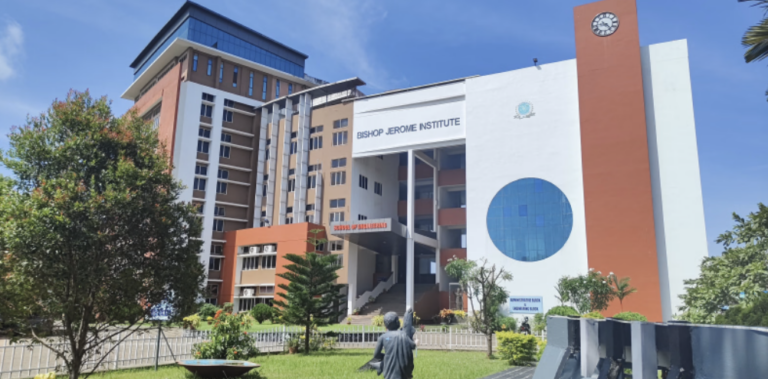
Bishop Jerome Institute, Kollam
2.5 lakh sq ft, three academic blocks
A new campus network across the Engineering, Management and Architecture blocks, about 2.5 lakh sq ft, built after a full audit of the old one.
- Kollam
- Education
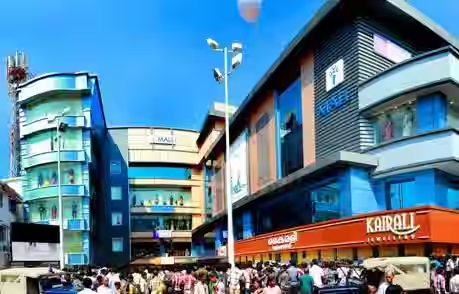
I Mall, Kollam
Head office and branch offices
A complete IT upgrade for the head office and branches: cabling, network and security, servers, email and phones, from one team.
- Kollam
- Retail
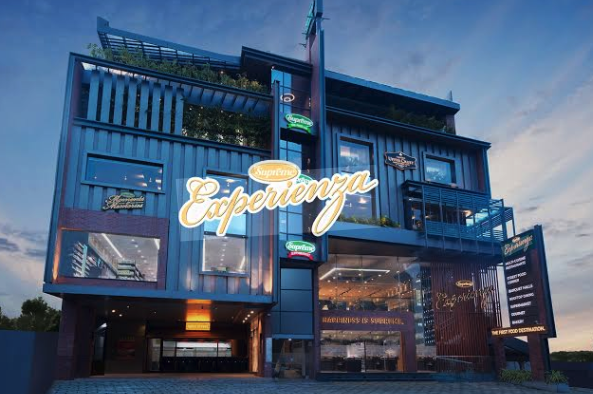
Supreme, Kollam
One secure network for the head office and every branch. Firewalls, VLANs for data, voice and video, and locked switch ports. Active Directory and a file server for central logins and files, and Wi-Fi run from one place.
Where we work
We deliver IT security assessment across Kollam (Quilon), Thiruvananthapuram (Trivandrum), Alappuzha (Alleppey) and Pathanamthitta, from our base in Kollam.
Questions we often get
Will the scans disrupt our systems?
We agree times and limits in advance and avoid tests that could disrupt live systems. Most scans run without anyone noticing.
How long does an assessment take?
It depends on the scope. We give you a timeline before we start.
Is this a certified audit?
No. It is a practical review. If you need a formal audit, for example by a CERT-In empanelled auditor or an ISO 27001 certification body, we can help you prepare for it.
Do you keep our data confidential?
Yes. We sign a confidentiality agreement before we start, share findings only with the people you name, and delete scan data at the end of the work.
Related services
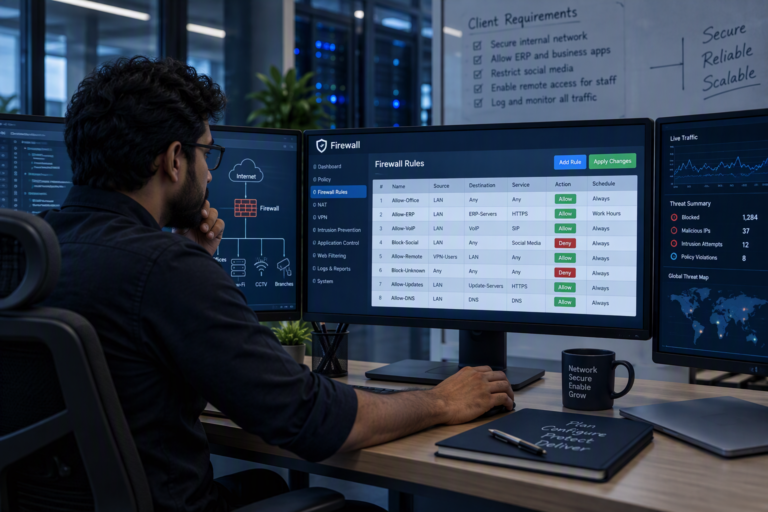
Firewall Configuration
Next-generation firewalls set up properly: web filtering, separate networks, VPN for remote staff, bandwidth control and logs.
- NGFW
- IPS
- VPN
- Web filter

Endpoint security
Business antivirus and EDR on every computer and server, managed from one console, with USB control and email protection.
- EPP
- EDR
- Device control
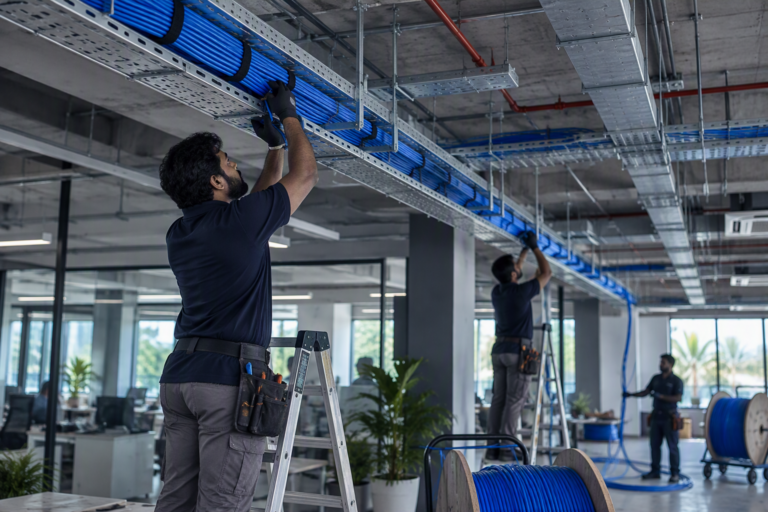
Structured cabling
CAT6 and CAT6A data cabling, I/O points, patch panels and racks. Every cable labelled at both ends and tested before handover.
- CAT6
- CAT6A
- I/O
- Racks